Encryption at rest and in transit
Check the safeguards applied while the file is held and while it travels to its recipient.
SECURE DATA STORAGE
Keep the master document in its approved repository. When a client or supplier needs a copy, decide who may receive the release, where it may be held and when access should end.
01 / A CLEARER ARCHITECTURE
Check the revision before export. Set recipient permissions on the exchange separately from the access rules on the original folder.
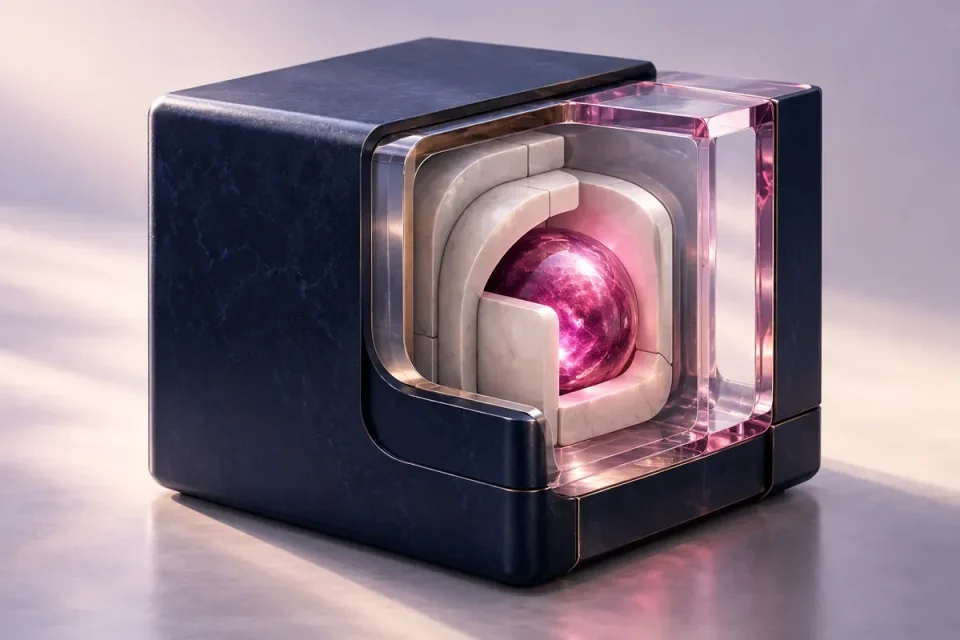
AES-256 applied to data as it moves and as it sits. This is the baseline, and a supplier who cannot describe it plainly is worth further questions.
Distributing protected shards across separate destinations means that access to a single location does not yield a usable file. It is a structural protection instead of a cryptographic one.
Named accounts, role-based permissions and MFA where the material warrants it. Most storage incidents are access incidents instead of cryptographic failures.
Choices over data location, in suitable configurations, so the arrangement can match your own residency and contractual requirements.
02 / A PROTECTED JOURNEY
Ask where files are held, how they are protected and which recovery options are available for your configuration. Confirm the answers against the project requirements.
Check the safeguards applied while the file is held and while it travels to its recipient.
On Enterprise, ASR distributes protected fragments and restores the file for the verified recipient.
Trusted with valuable business data
03 / THE DETAILS MATTER
Keep the exchange reference with the approved revision. When a partner asks for another copy, check what was already issued and to whom.
Review the exported file and its audience independently of permissions on the original folder.
Set a review date for the release and agree how the recipient will handle downloaded copies.
Record the exchange reference beside the master revision so colleagues can trace the delivery.
CUSTOMER PERSPECTIVES
All customer stories ↗“I would highly recommend MX to anyone looking to send and receive secure data quickly and efficiently.”
04 / TWO DIFFERENT JOBS
Review the access window at the end of the assignment. Agree how the recipient will handle downloaded copies and apply your retention rules to the master.
Check the project and owner before accepting an incoming document into storage.
Confirm who may retrieve the stored version and who is responsible for its retention.
A focused role in your architecture. Use your primary repository for long-term storage and backup. MX focuses on controlled file exchange and the availability of files during that exchange.
GOOD QUESTIONS. CLEAR ANSWERS.
Practical answers about secure data storage and where MX fits.
Protect sensitive information while it is being exchanged, with encryption, named access and configurable availability. MX complements long-term repositories by concentrating on the controlled handoff.
Named-recipient access, authentication, permissions and expiry settings help define the exchange. Activity records let your team review what happened. The available configuration should be matched to your requirements.
Keep creating, editing and storing files in the systems your team already uses. MX focuses on controlled handoffs, rather than background synchronisation, live co-authoring or permanent backup.
Try the MX feature set for 7 days with up to 5 users. No credit card is required.
YOUR NEXT EXCHANGE STARTS HERE
Put better controls around your next sensitive file exchange. See how MX fits your organisation's workflow.